For many SME CEOs, hiring a full-time Chief Information Security Officer (CISO) is a non-starter. The math simply doesn't work: a six-figure salary + benefits + recruitment fees for a role you might not need 40 hours a week.
So, you delegate it to the IT Manager. And that is where the risk begins.
The "IT Security" Trap
IT builds things. Security checks things. When you ask your IT Manager to be your CISO, you are asking them to mark their own homework.
In 2026, with NIS 2 and DORA enforcement hitting supply chains hard, this conflict of interest is no longer just a bad idea—it's a compliance failure.
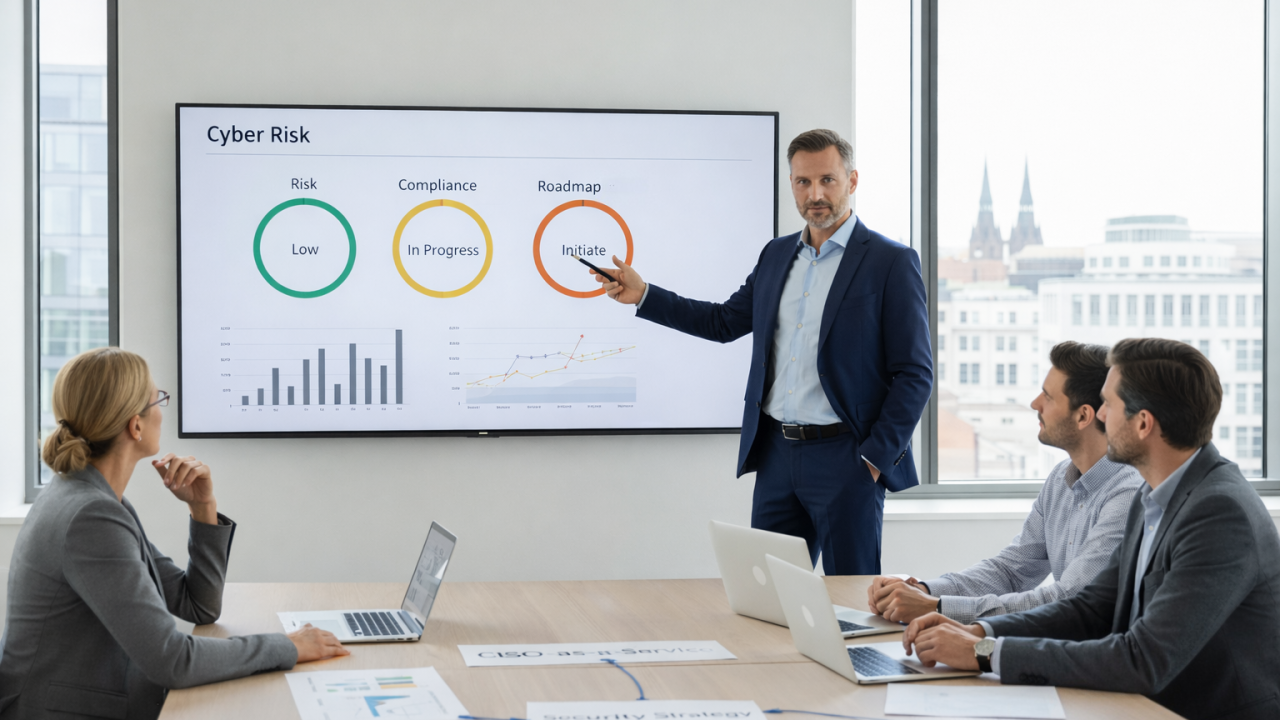
Enter CISO-as-a-Service (vCISO)
It's not just "rent-a-CISO." It is the most efficient operational model for high-growth SMEs.
At Digisoter, we see CISO-as-a-Service delivering three things that a junior full-time hire cannot:
Instant Experience, Zero Ramp-Up: You don't get a learner; you get a veteran who has managed crises, audits, and boards before. You pay for their output, not their presence in a seat.
Strategic Independence: A vCISO sits outside your IT politics. We report risk objectively to the Board/CEO, ensuring you get the unvarnished truth about your posture.
Flexibility by Design: Need heavy lifting for an ISO 27001 audit in Q1? Scale up. In "maintenance mode" for Q2? Scale down. You consume leadership as a service, not a fixed cost.
The ROI is Simple : For the cost of a mid-level IT admin, you get Board-level assurance.
Don't settle for "good enough" security because you think you can't afford the leadership. In 2026, fractional is the new functional.
Is your security leadership scaling with your business, or holding it back?