Cyber Governance & Continuous Assurance-as-a-Service, with senior CISO accountability as the differentiator.
Your job is to run the compagny. Not to be its CISO
Stay ahead of regulatory shifts, emerging threats, and industry best practices with insights from our team of security experts.
Your job is to run the compagny. Not to be its CISO

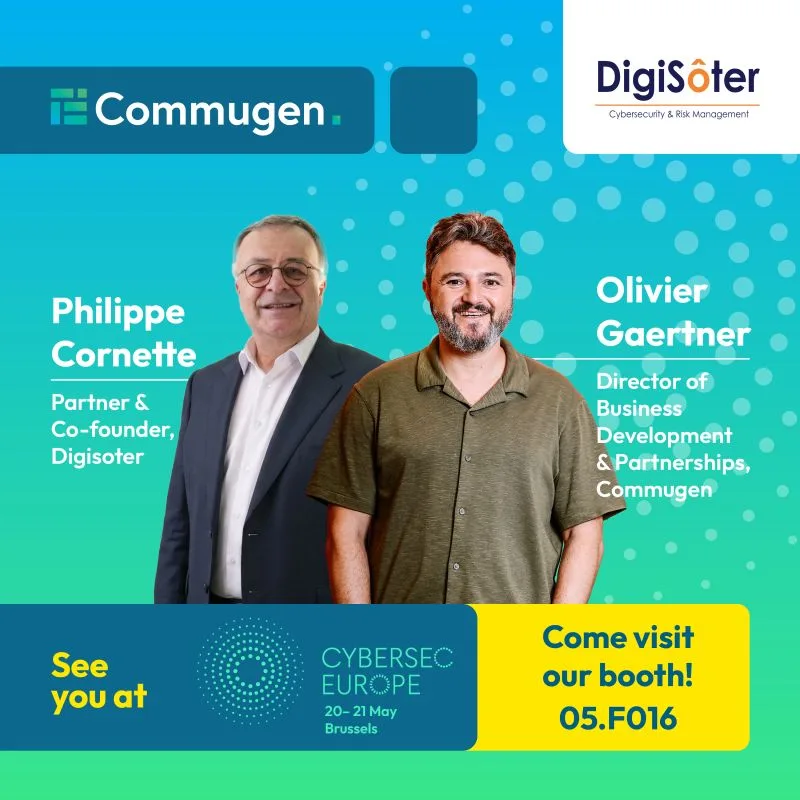
On 20 and 21 May, I will be at Cybersec Europe in Brussels together with our partner Commugen.
The EU just raised the stakes: now CISO need to speak the language of the product team, the engineering sprint, and the software supply chain. Most were never trained for this. Many were never even asked. The CRA (Cybersecurity Resilience Act)

ANSSI has published ReCyF — the recommended measures to meet NIS 2 security objectives in France. At DigiSôter, we have been applying this kind of framework in Belgium for two years.

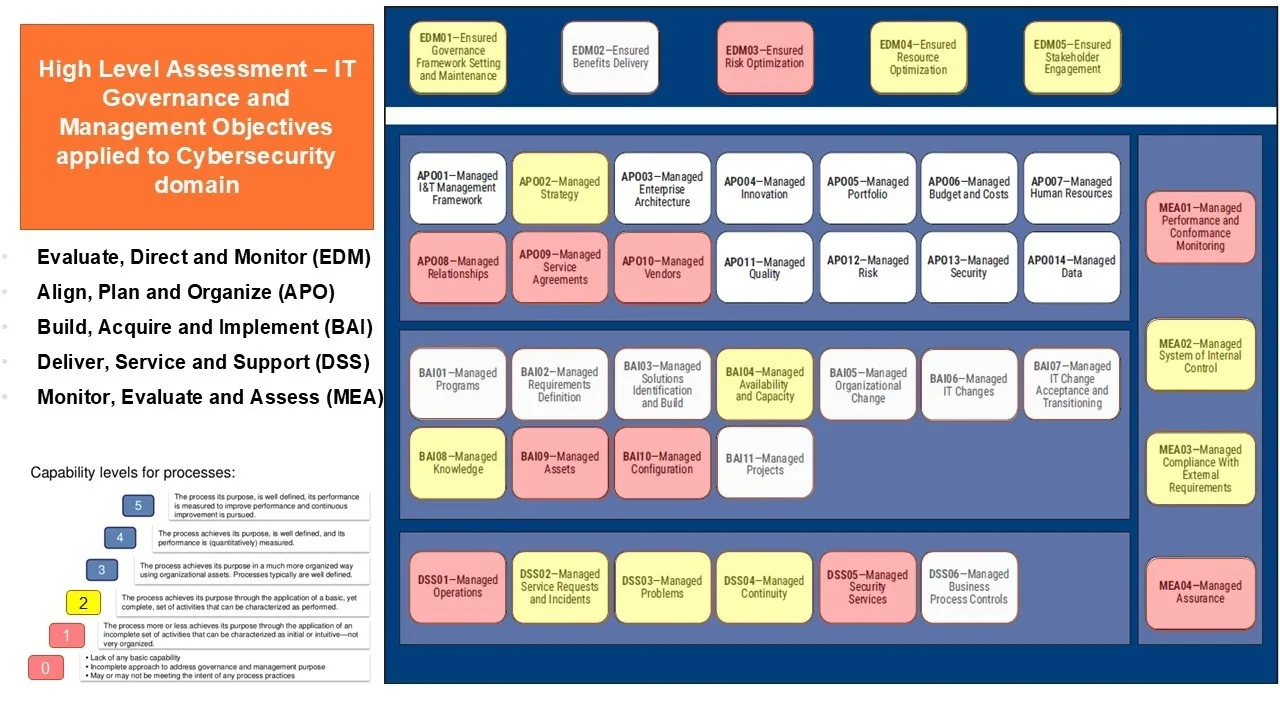
Every regulation keeping you up at night, NIS2, DORA, CRA, and every certification you are chasing, ISO 27001, they all assume one thing: that your IT operates like a mature organization. Most do not. And no security product on the market will fix that.

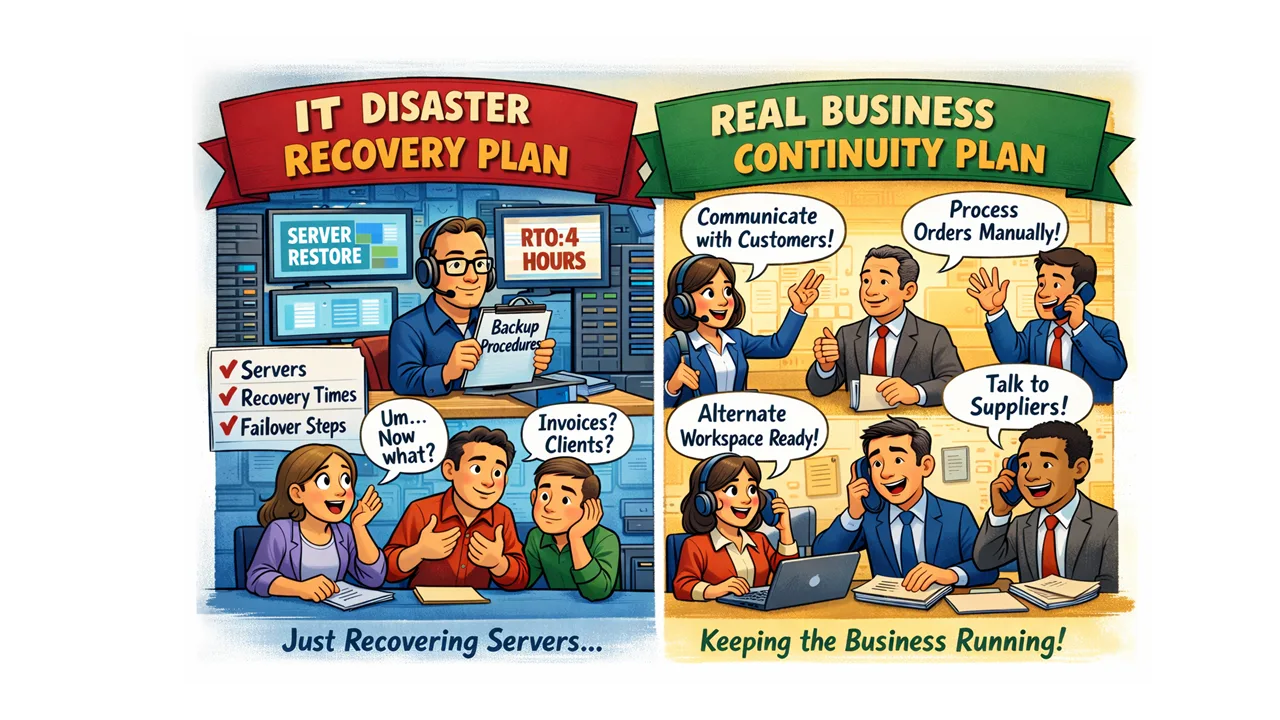
Your Business Continuity Plan has a problem. It is 40 pages long, covers every database and failover cluster in the organisation, and cannot tell your leadership team what to do in the first hour of a real crisis.
DigiSôter est un cabinet de conseil belge en cybersécurité spécialisé en gouvernance, gestion des risques, conformité (GRC), et proposant des services tels que CISO à la demande, conformité ISO 27001 et NIS 2, ainsi que des évaluations de sécurité, avec une approche indépendante des fournisseurs.
Your CISO is asked to prevent the unpredictable, manage the invisible, and explain the unexplainable. Then you are surprised when they burn out after 18 months.

Many SMEs recognize the need for improved cybersecurity, but few can afford a full-time Chief Information Security Officer (CISO). CISO as-a-Service addresses this gap by providing smaller organizations with access to experienced security leadership on a flexible, part-time basis.
Your biggest security perimeter is no longer your firewall. It is your suppliers. In a world of cloud, outsourcing, and interconnected operations, trust is essential, but trust without verification is not governance. It is hope.
Before you read any further, test your governance in 10 seconds: Who can access your plant remotely, under which conditions, and how fast can you cut them off? If the answer is not immediate, you already have an exposure problem.

Your data generated in Europe is very likely hosted on infrastructure subject to United States jurisdiction, and in practice, you have limited control over this reality.
Most incident response plans are designed to satisfy auditors, not to function at 02:00 am when everything is burning. If you have not tested your crisis response, you do not control the risk, you only document it.
The next cyber incident in your company will not start in the data center. It will start on the shop floor. Unmanaged remote access, shared PIN codes, forgotten USB sticks, and flat OT networks are obvious risks.
Implementation roadmaps, obligation mapping, and Belgian transposition specifics.
Certification journeys, common pitfalls, and ISMS maintenance.
IT/OT convergence risks and ISA/IEC 62443 practical guidance.
Board reporting frameworks and security programme maturity.
TPRM methodologies and DORA third-party requirements.
Access detailed compliance guides, readiness checklists, and maturity assessment templates. Free, requires email.
Coming soon. Subscribe to our newsletter to be notified.
Subscribe to our newsletter for monthly updates on NIS2, ISA/IEC 62443, emerging IT/OT threats, and strategic risk management.